





Table of contents
User Provisioning
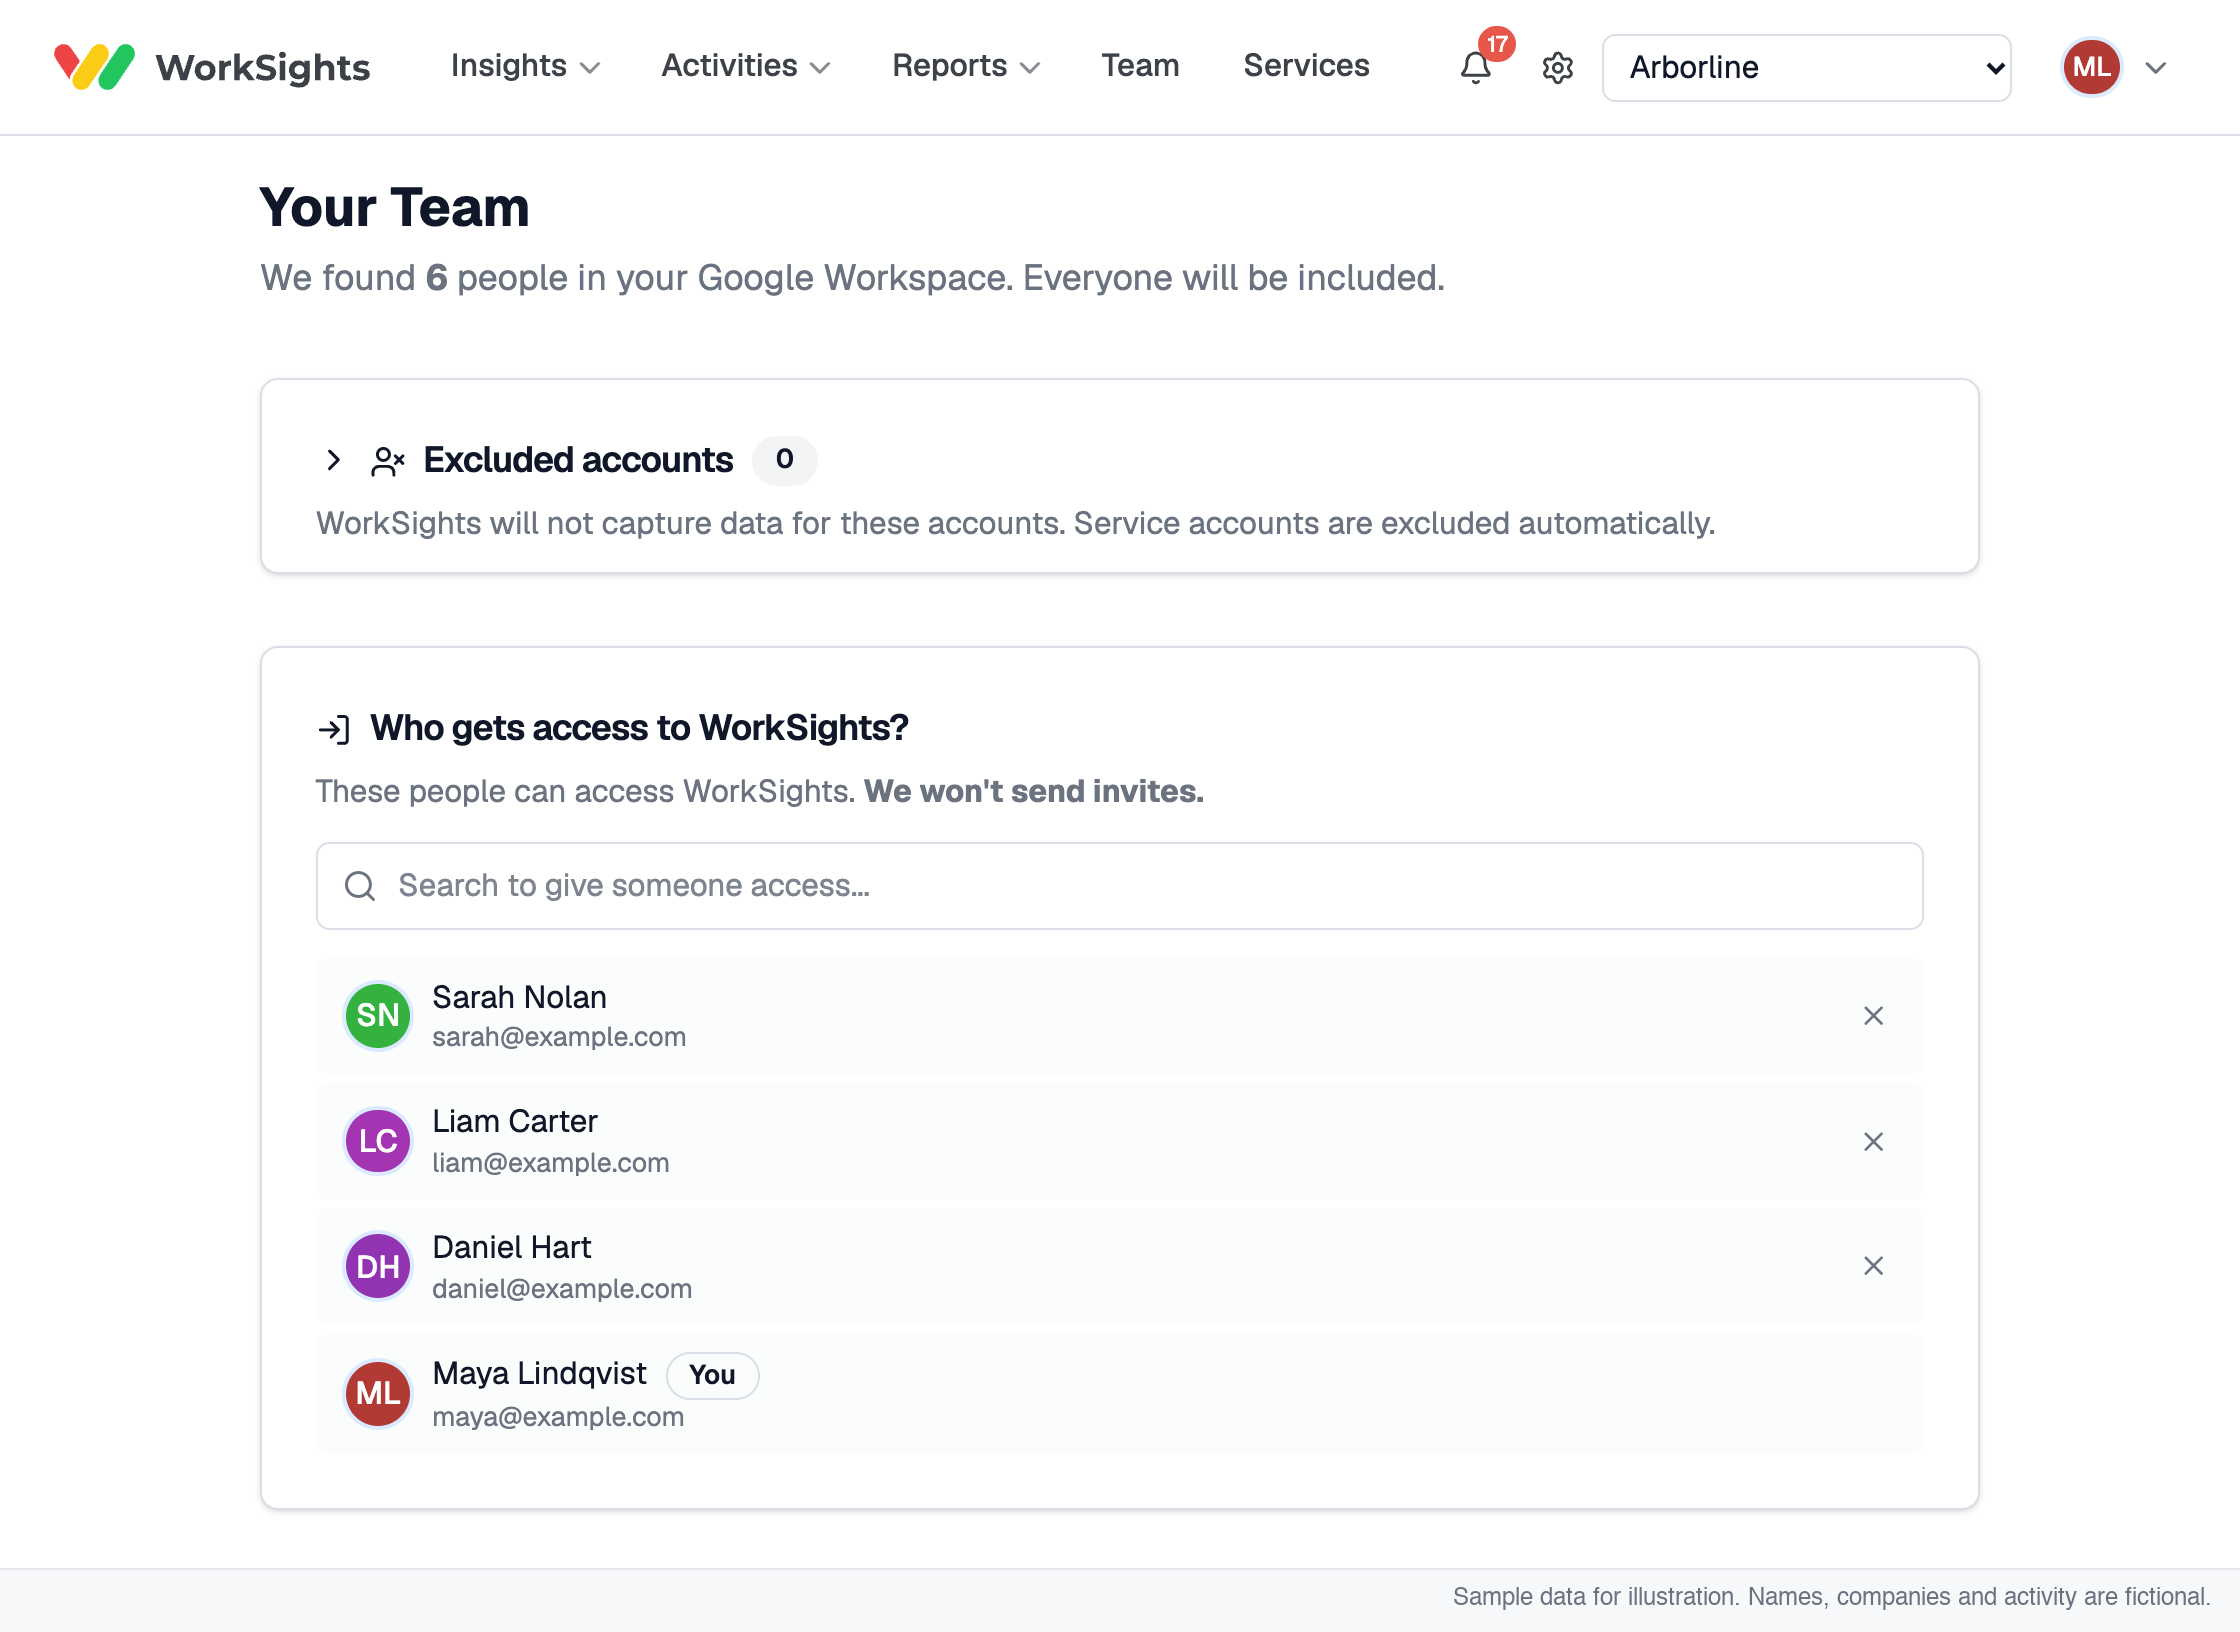
User Provisioning is where WorkSights aligns your connected Google Workspace or Microsoft 365 directory with your WorkSights workspace. When your domain is connected, WorkSights imports users directly from your directory and presents them for review by an Admin.
Provisioning makes sure WorkSights reflects the real structure of your organization: who is included, how identities map, and which accounts take part in reporting.
Provisioning States
WorkSights uses four states to define how each imported identity is handled.
- New - a new WorkSights profile will be created for this person.
- Link - the imported identity matches an existing WorkSights profile and will be connected to it. Use this when an employee already exists in WorkSights or when consolidating several email addresses.
- Blocked - the user will be excluded from WorkSights. Useful for service accounts, external identities, test mailboxes, or any account that should not appear in reporting.
- Already Linked - WorkSights has automatically recognized and matched this identity to an existing profile. No action is needed.
How WorkSights Matches Users
WorkSights compares imported identities to existing profiles by primary email address and domain alignment. If it finds a match, the user appears as Already Linked. If not, the user appears as New until an Admin reviews them.
Admins can set a user to Link when an imported email belongs to someone who already exists in WorkSights under a different address or profile. This prevents duplicate profiles and keeps reporting consistent.
Roles
After provisioning, Admins can assign each user a role that defines their level of access inside WorkSights.
WorkSights includes standard roles: Member, Manager, Executive, Admin, and Owner. Custom roles combine Admin, Executive, Manager, and Member permissions. Admins and Executives can create and edit custom roles. Job categories, such as Engineering or Sales, are managed separately and do not grant access permissions.
Reporting lines are set separately. See Assign Manager Relationships for how to define your organization's hierarchy.
Activity Processing
A user begins showing activity in WorkSights once they are provisioned. Activity includes email metadata such as subject, recipients, and timestamps; calendar events; and other signals from connected tools such as Teams messages, SharePoint and OneDrive interactions, Google Calendar events, and login activity.
WorkSights assigns timezone and scheduling context from the available metadata.
Users who are Blocked or not yet reviewed do not appear in reporting and have no activity processed.
Directory Sync
WorkSights stays in sync with your connected directory. When changes occur:
- New employees appear as New in provisioning and wait for an Admin's review.
- Users removed from your directory lose login access to WorkSights.
- Admins can re-map users, adjust roles, or block accounts at any time.
You can return to provisioning whenever your organization changes.
What Happens Next
Once User Provisioning is complete, continue to Assign Manager Relationships. This step defines your organization's reporting lines so that reporting in WorkSights reflects your real hierarchy.
Related Guides
Assign Manager Relationships - define reporting lines after provisioning is complete
Account Details - edit your account information
Team List - manage users, roles, and category assignments after setup is complete